Understanding Recurring Reports
Recurring reports display a zone-based summary of traffic and attack information on a periodic basis (daily, weekly, or monthly) for a given group (or a single selected zone). A manual report will display the same information, using an arbitrary start and stop time.
Report Header
The header will include your customized logo and report name. It will also contain the name of the group or zone the reports was run on, "Daily", "Weekly", "Monthly" or "Manual" to identify the report period, and the start and end times used for the data in the report. The start and end times, and all other timestamps used in the report, will be displayed in the timezone selected for the report.
Traffic Overview
The overview provides summary information for the group (or just the selected zone if run on a single zone) during the selected time period.
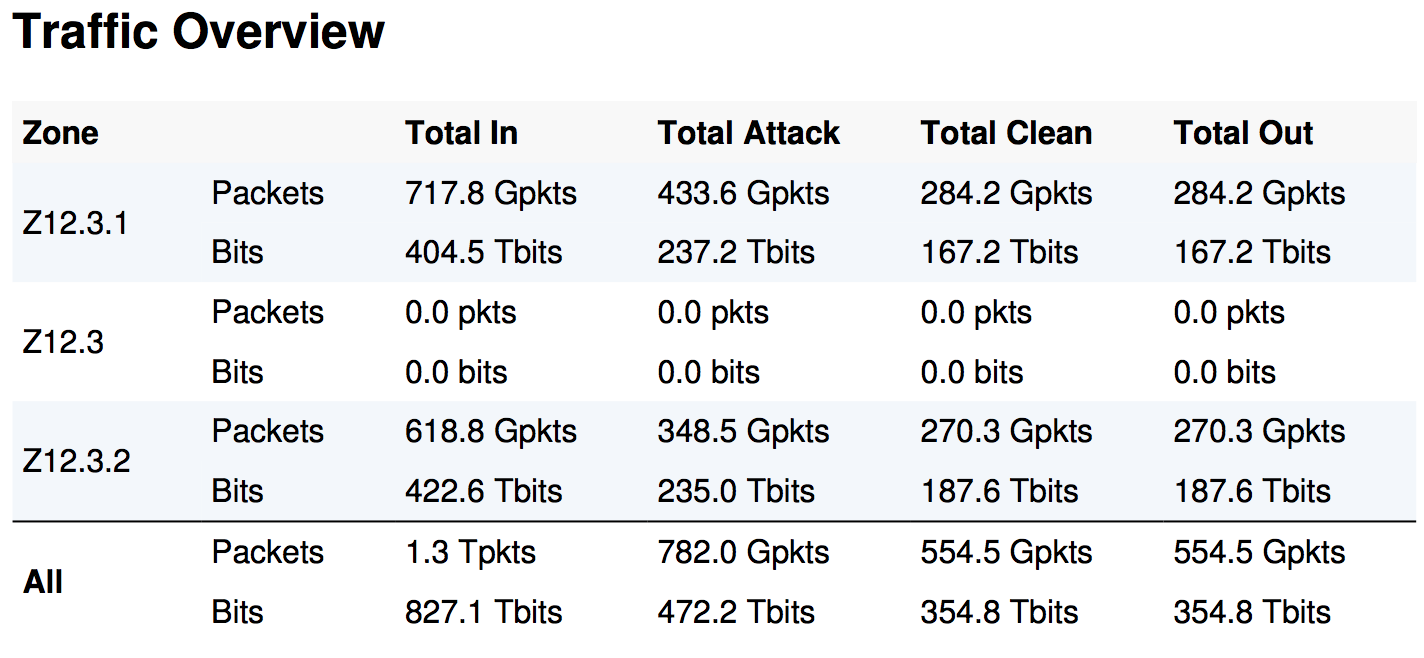
Each Zone's gross traffic volumes are listed individually next to their name in both packets and total bits.
- ALL- contains the sum of all traffic to the Zones for each category, and therefore the total traffic to the Group. If run on a Zone only, this will be the same as that Zone's values
- Total In- lists the total volume of traffic seen for the Zone.
- Total Attack- this is the volume of traffic which is deemed an attack.
- Total Clean- lists the volume of traffic that is not considered an attack.
- Total Out- this is the volume of traffic which is allowed to pass through the zone. This value could be greater than the **Clean **value if attack types are in monitor mode. In that case it will be detected as an attack but still allowed to pass through.
Network Traffic
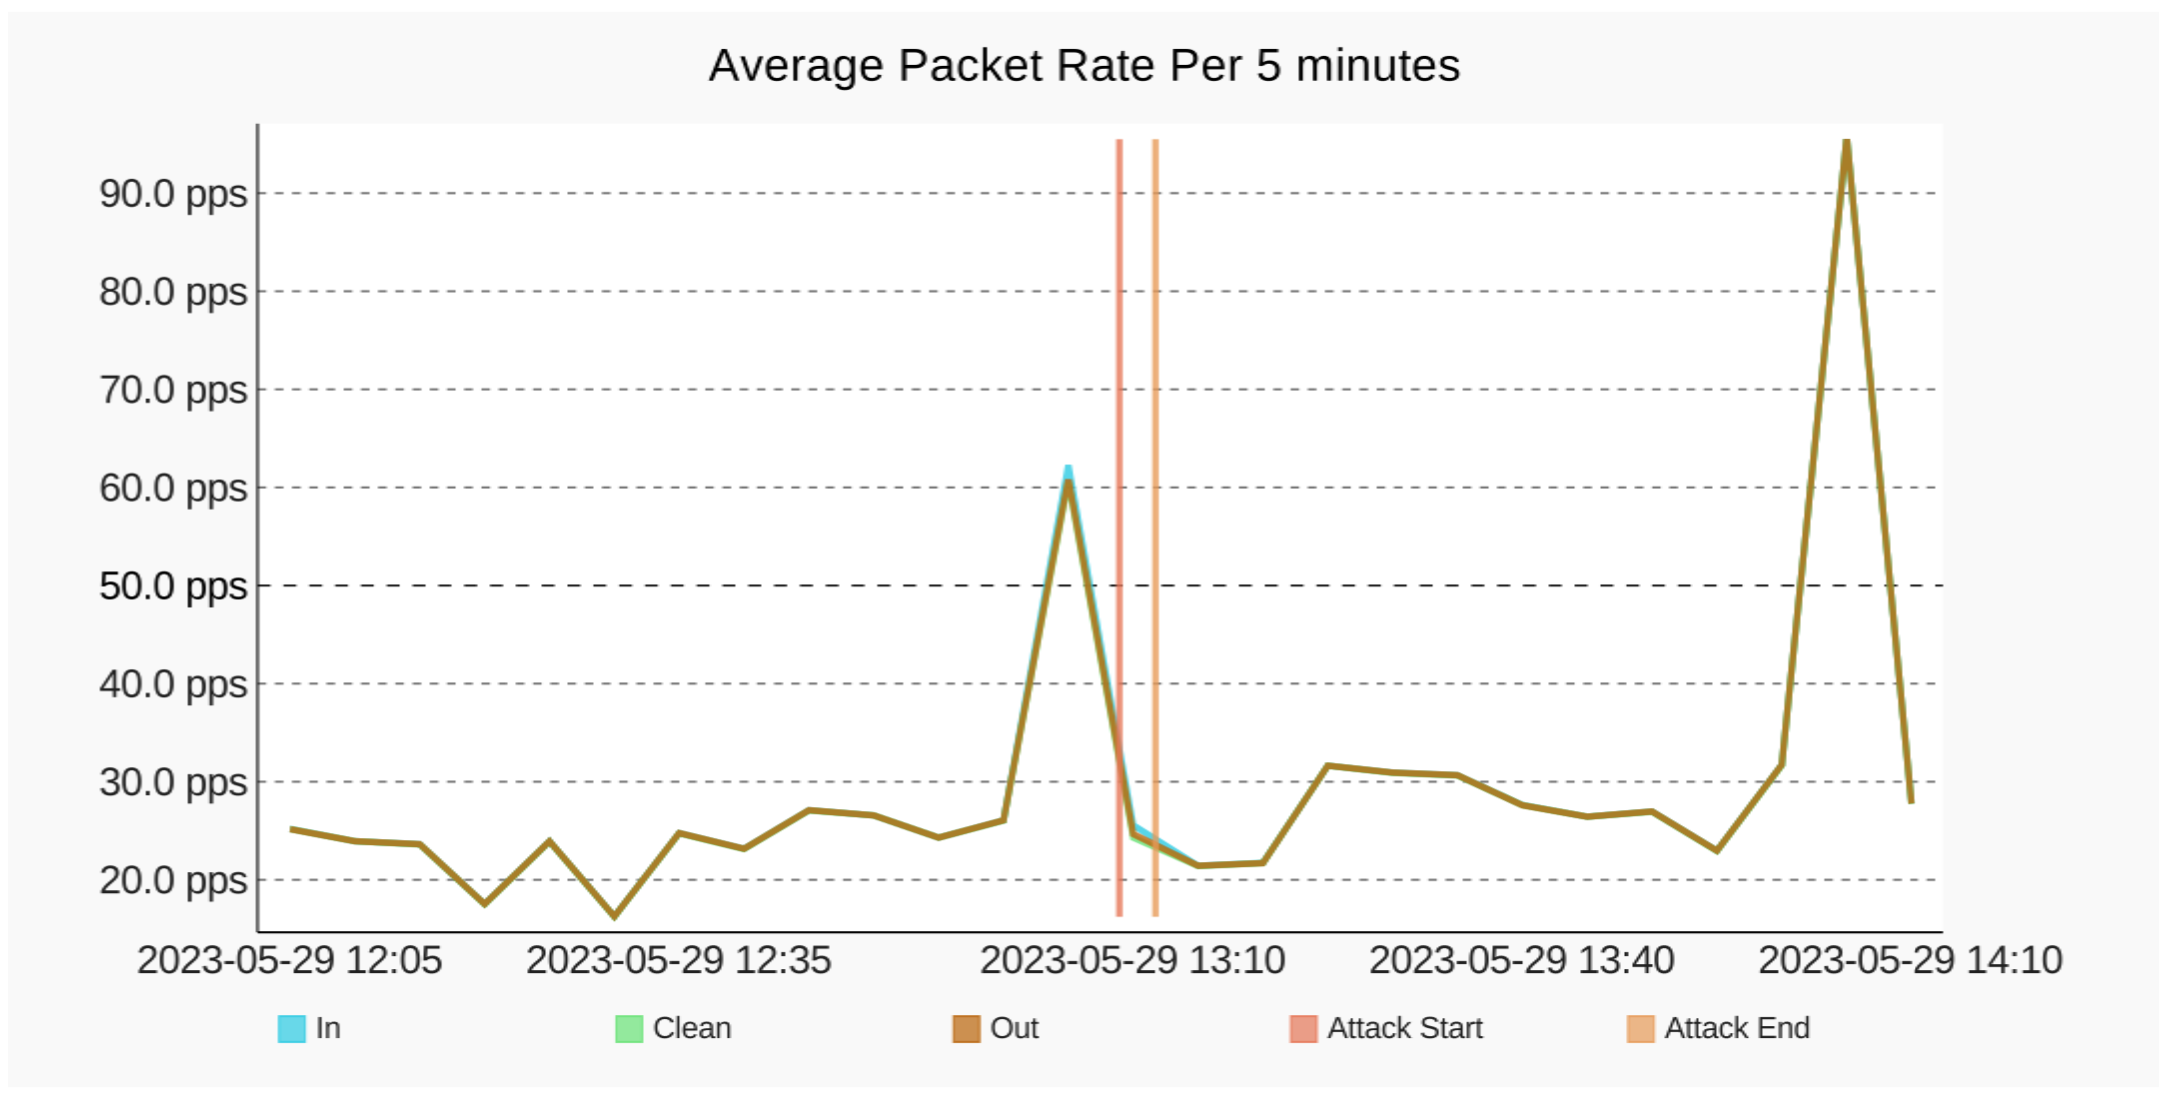
There will be packet and bit based packet graphs for the selected time period, aggregated for all zones (if run on a group) or the selected zone. The graph will show In, Clean, and Out using available time data:
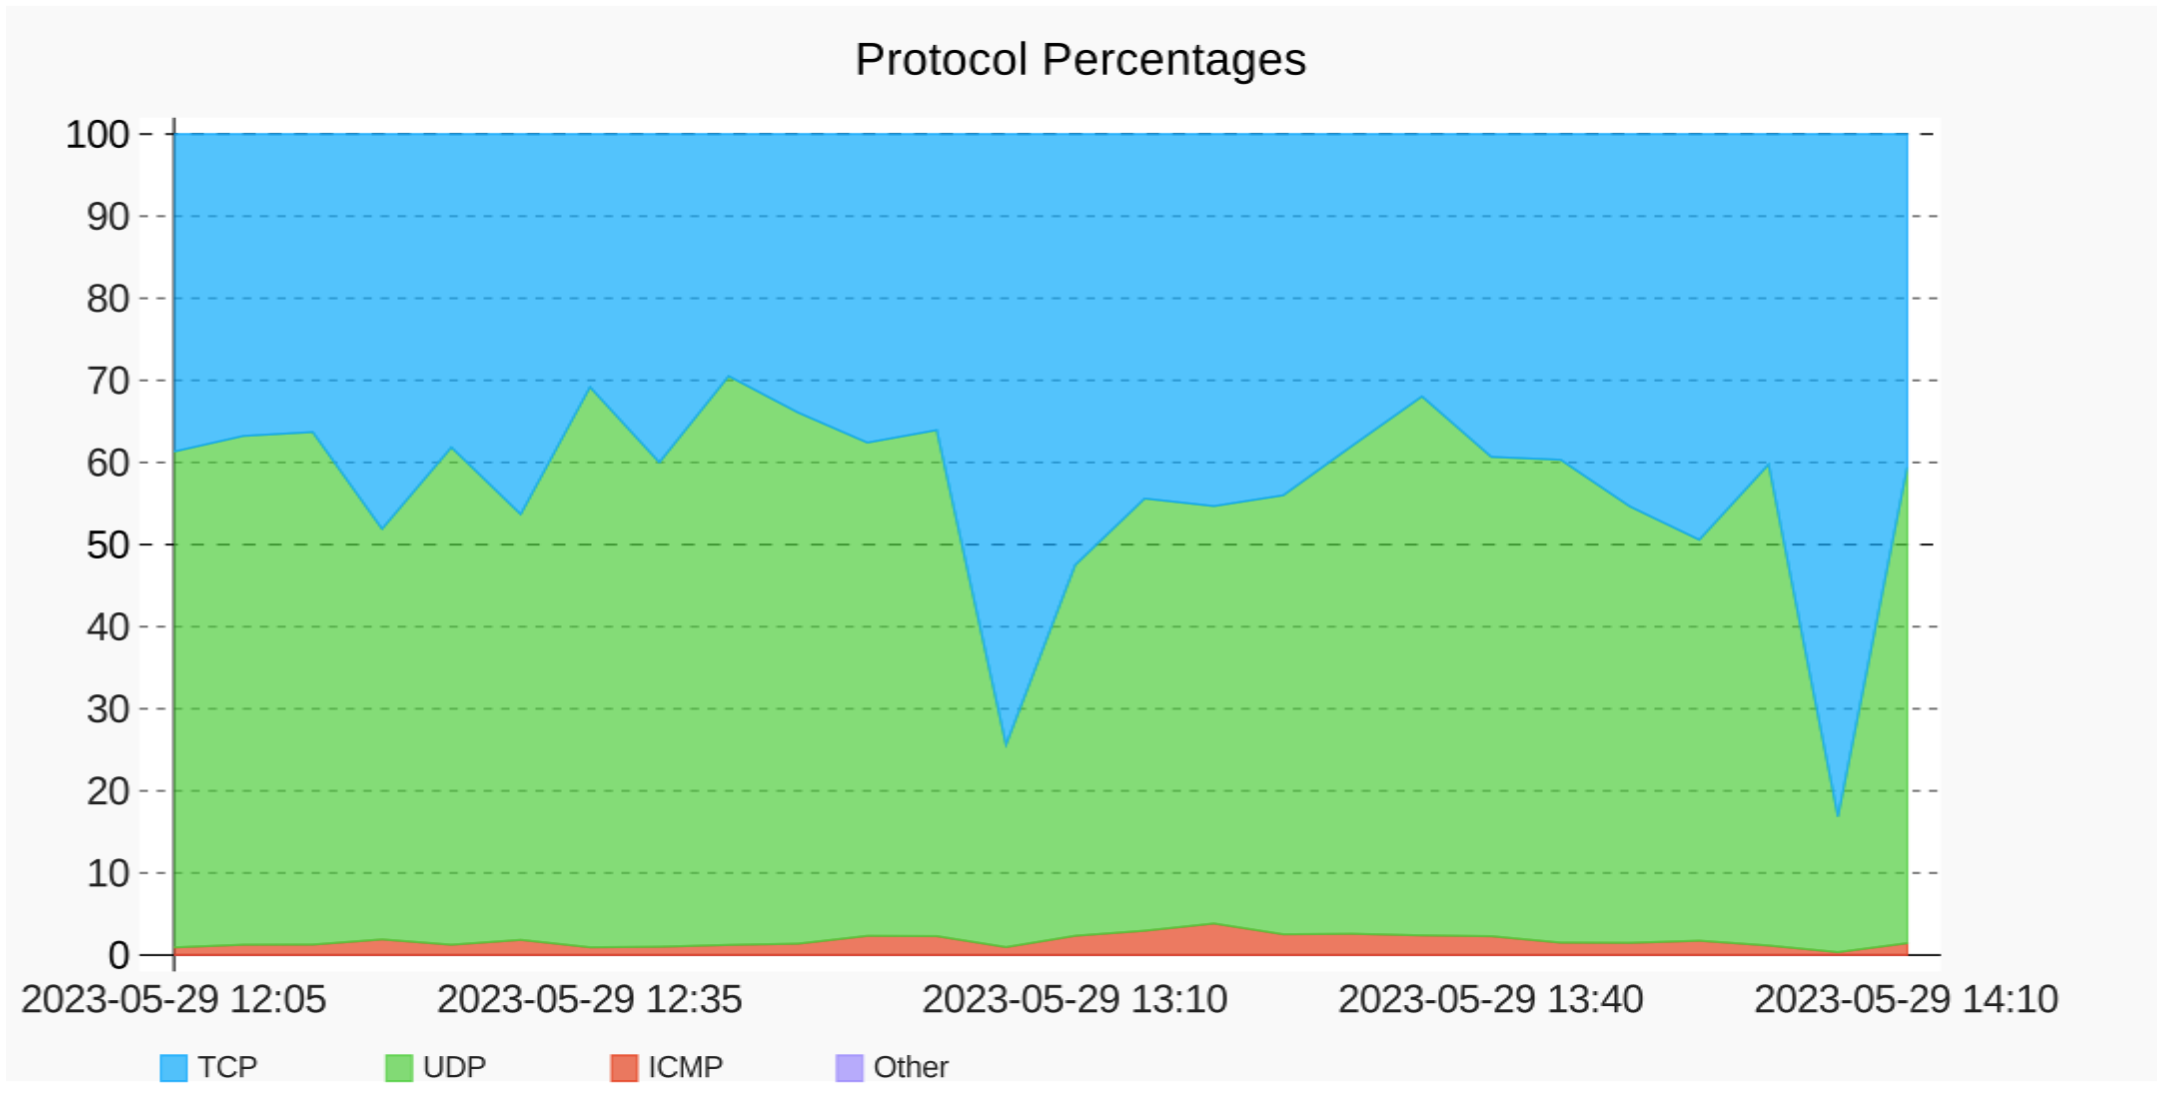
This section also includes a breakdown of the group's (or single zones) protocol percentages by TCP, UDP, ICMP, or Other.
Attack Breakdown
This section lists all attacks contained within the selected time period. Both the start and end time for the attack need to be within the report period in order to be listed.
- Attack Type- The attack type.
- Total Attacks- The total number of attacks of this type contained within this time period.
- Total Attack Packets- The total number of attack packets detected for this attack type.
- Total Attack Bits- The total number of attack bits detected for this attack type.
Top Attacks by Packet Count
This section will list the ten biggest attacks by packet count. These attacks only need to transit the reporting period (not necessarily occur entirely within the window):
- Rank- The rank, 1 to 10, by packet count of the attacker.
- Victim Address- The victim's IP address.
- Attack Type- The type of attack, according to the 25 Mitigation Methods.
- Total Attack Packets- The total number of attack packets of this type that were detected.
- Total Dropped Packets- The total number of attack packets of this type that were dropped.
- Total Attack Bits- The total number of attack bits of this type that were detected.
- Total Dropped Bits- The total number of attack bits of this type that were dropped.
- Start Time- The start time of the attack.
- End Time- The end time of the attack.