Traffic Summary - Device Breakdown
If your user has device permissions, you will be able to see the Traffic Summary - Device Breakdown widget on the mitigation status tab. This summary is a chart section which can be configured to display multiple types of traffic graphs on a per device basis.
When displaying this section, each chart will display an independently toggleable line of data for each filter device configured for this zone.
Basic Controls
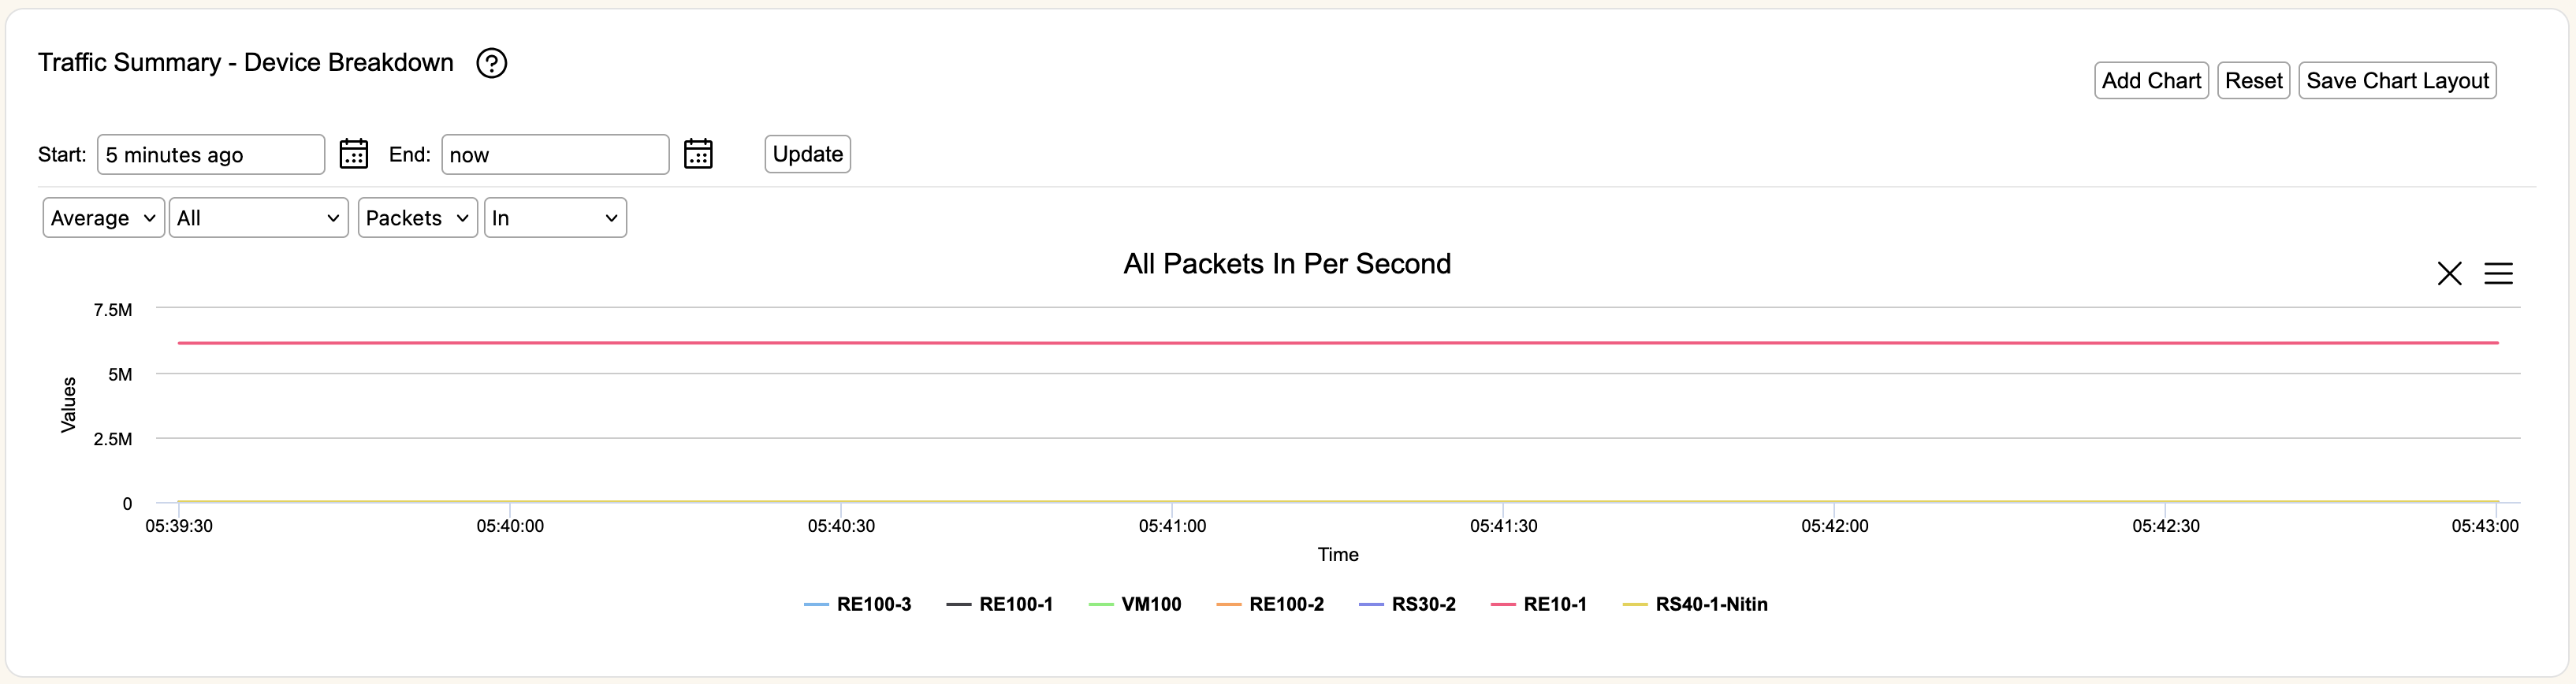
Add Chart will create a new chart that can be set to a new data type independent of any existing charts, over the same selected time period. By default, you will see a chart of Average All Packets In traffic for the past five minutes. Save Chart Layout will change the default to your currently open set of charts. Hitting Reset will bring it back to this default set of charts, preserving any new times you've entered.
Start and End are the times used to create the charts in that group. You can use the icon to select a specific date and time, or you can write an entry in the format "X year/month/week/day/hour/minute ago", or use "now" to indicate current time. You can use the mouse to click and drag on the chart to zoom in to sections of the chart without having to set a new time period. Click Reset Zoom to bring it back to the original settings.
Update will refresh the graphs if you have changed the Start, End or Traffic Categories settings. Graphs, by default, will refresh themselves based on the time period displayed and the number of ticks. The refresh time of the graph displayed will be listed above the graph area.
Below the update button is a series of dropdown menus indicating the displayed traffic type. More information on this is in the Traffic Categories section below.
The two icons shown on a chart allow you to Delete (cross icon), or Export (three bar icon) that chart. When using Export, you can immediately print the chart or export it to a variety of graphics formats.
Traffic Categories
Each chart in this section can be configured to report on a different type of data from each device in the zone. From left to right, the menus are:
Aggregation- Starting in 8.3.0, rWeb aggregates reported traffic from its original 30 second windows into 5 minute, 1 hour, and 1 day views (with independent data retention settings).
rWeb will automatically try to pick the best resolution of data for the Start and End times selected. For everything except the 30 second windows (which report the same thing for both settings):
- Average- 5 minute data will show you the average of the contained 30 second reporting. 1 hour and 1 day will average across their contained 5 minute window data.
- Max- All views will show the peak data captured by any 30 second data within their window.
Traffic Type- You can select by traffic for a number of types:
- All- All traffic types.
- IPv4- Only IPv4 traffic.
- IPv6- Only IPv6 traffic.
- IP Frag- Any IP traffic that has been fragmented.
- TCP- Only TCP protocol traffic.
- UDP- Only UDP protocol traffic.
- ICMP- Only ICMP protocol traffic. This encompasses both ICMPv4 and ICMPv6 traffic, which are technically separate protocols.
- TCP SYN- Only TCP packets with the SYN flag set.
- TCP SYN ACK- Only TCP packets with the SYN ACK flags set.
- TCP ACK- Only TCP packets with the ACK flag set.
- TCP FIN- Only TCP packets with the FIN flag set.
- TCP RST- Only TCP packets with the RST flag set.
- Allowed- Traffic either to or from an allow listed address.
- Other- Any non-IP related traffic.
Rates- You can view traffic from two rate perspectives:
- Packets- Traffic will be reported in packets per second (pps).
- Bits- Traffic will be reported in bits per second (bps).
Mitigation- Traffic reported against its mitigation category. These categories are:
- In- All traffic coming into the Zone.
- Out- All traffic that is being passed on to destinations within the Zone.
- Attack- All traffic that is considered malicious attack traffic.
- Clean- All traffic that is considered clean traffic.
- Monitored- All traffic that is being flagged by mitigation measures in monitor mode.
- Dropped- All traffic that is being dropped by filter devices and not forwarded.